Windows Exception Handling
4 min read
Every article, searchable and filterable by tag.
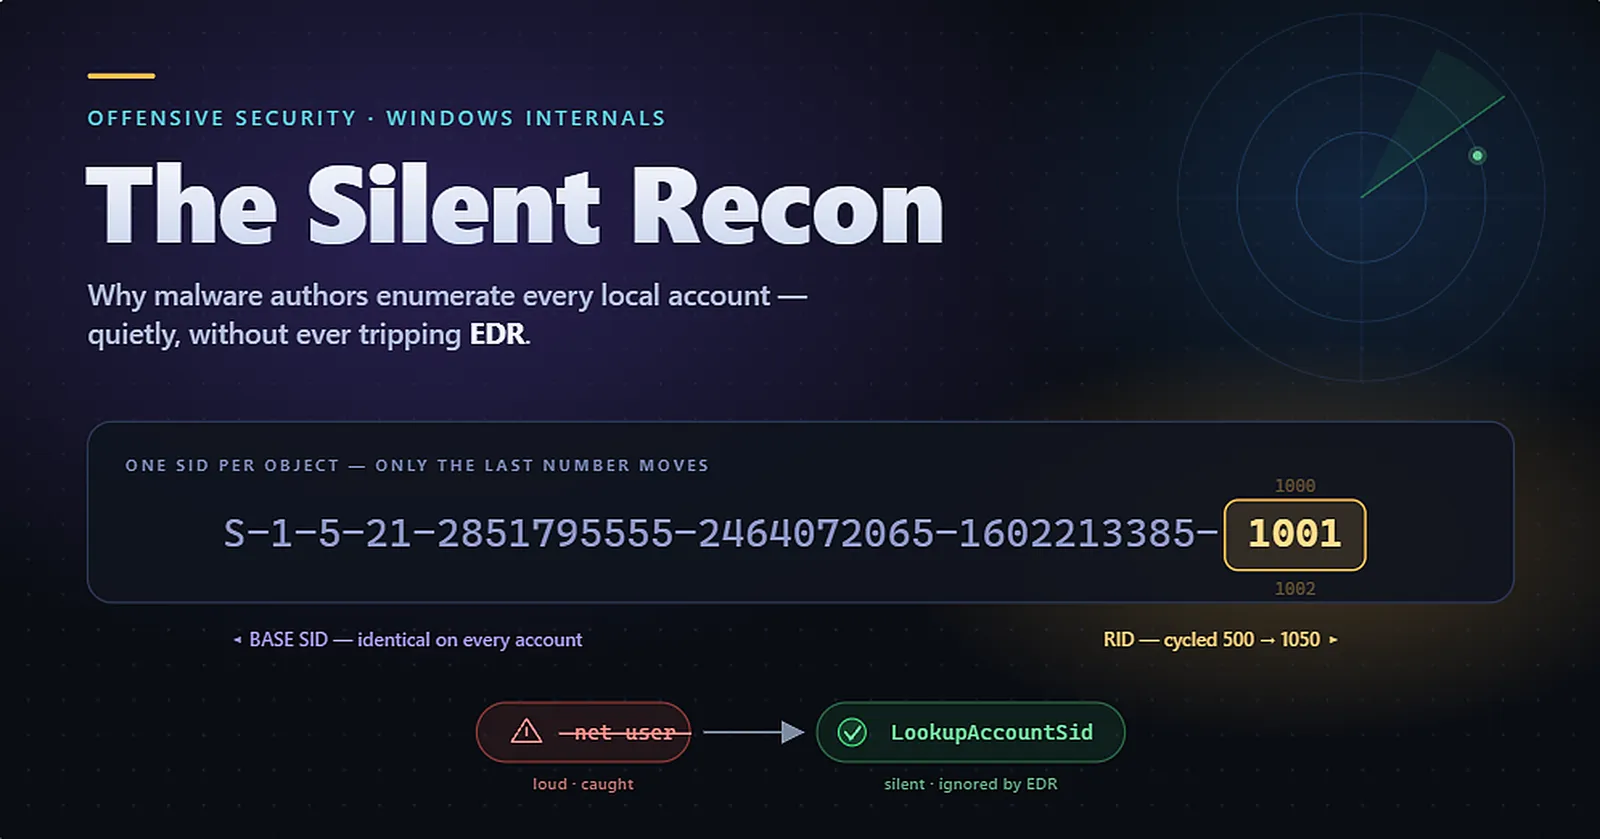
When an attacker lands a foothold on a Windows machine, their absolute first priority is discovery. They need to answer one crucial question: Who else is on…
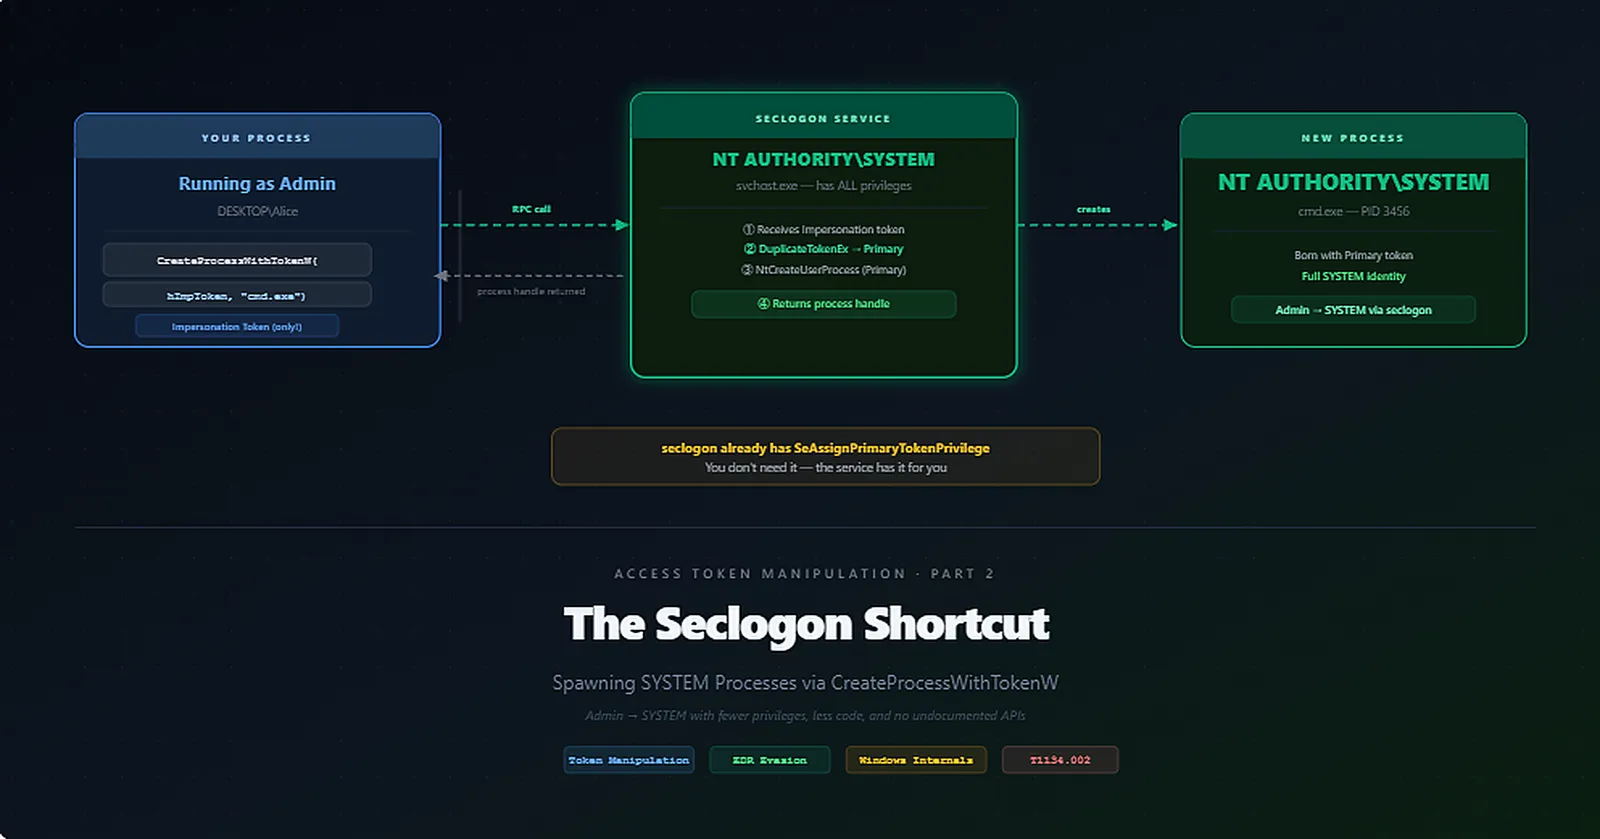
How a built-in Windows service does the dirty work for you — converting Impersonation tokens to Primary tokens behind the scenes, letting you spawn processes…
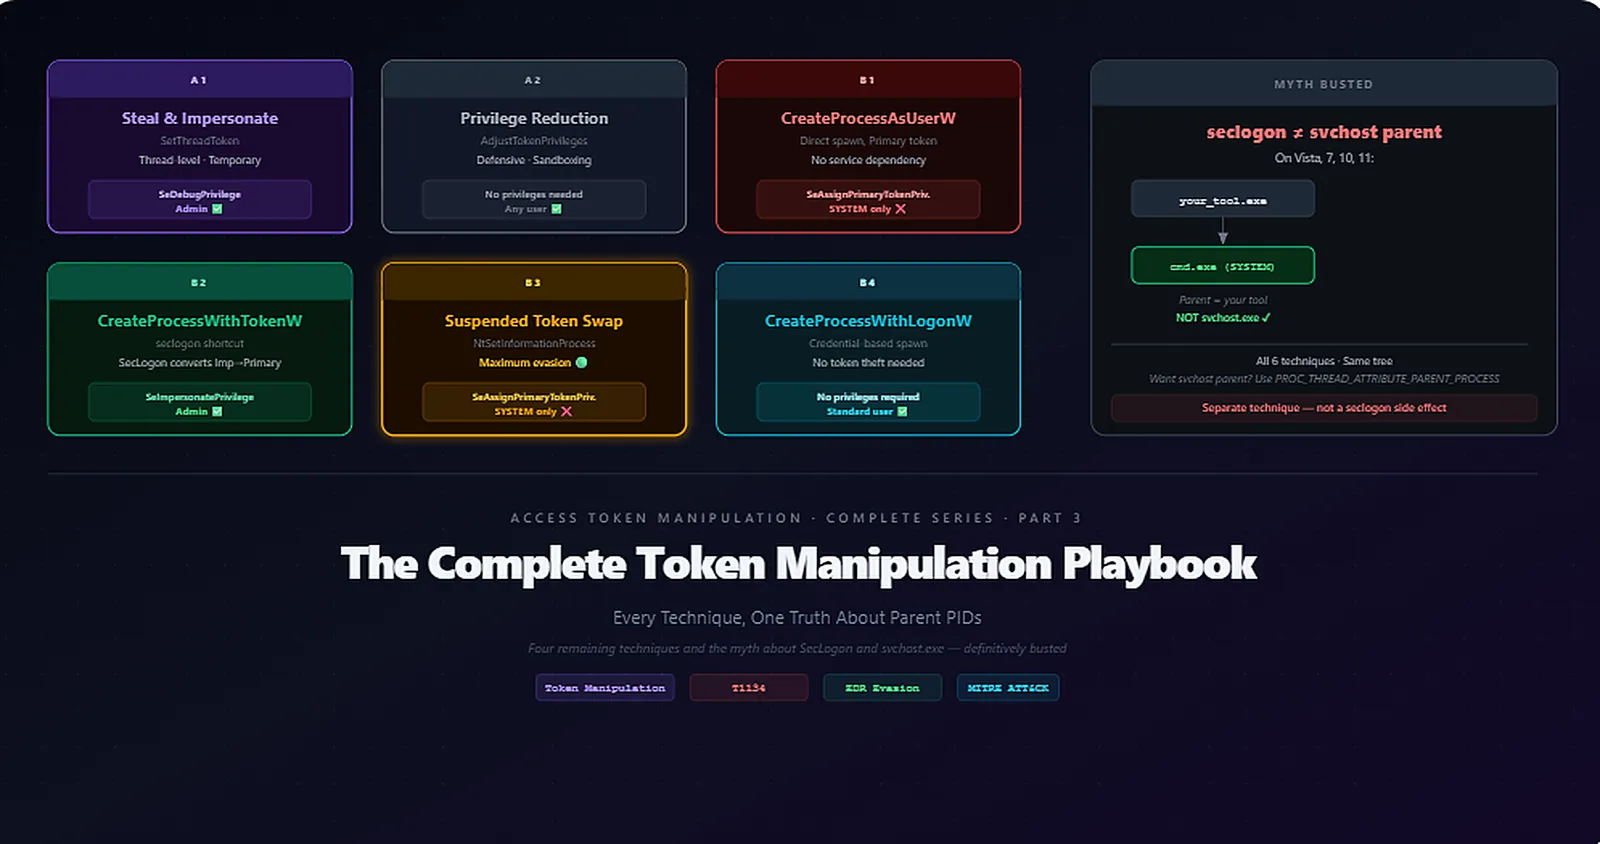
Four remaining techniques, a debunked myth about SecLogon and svchost.exe, and the definitive comparison of every way to abuse Windows Access Tokens.
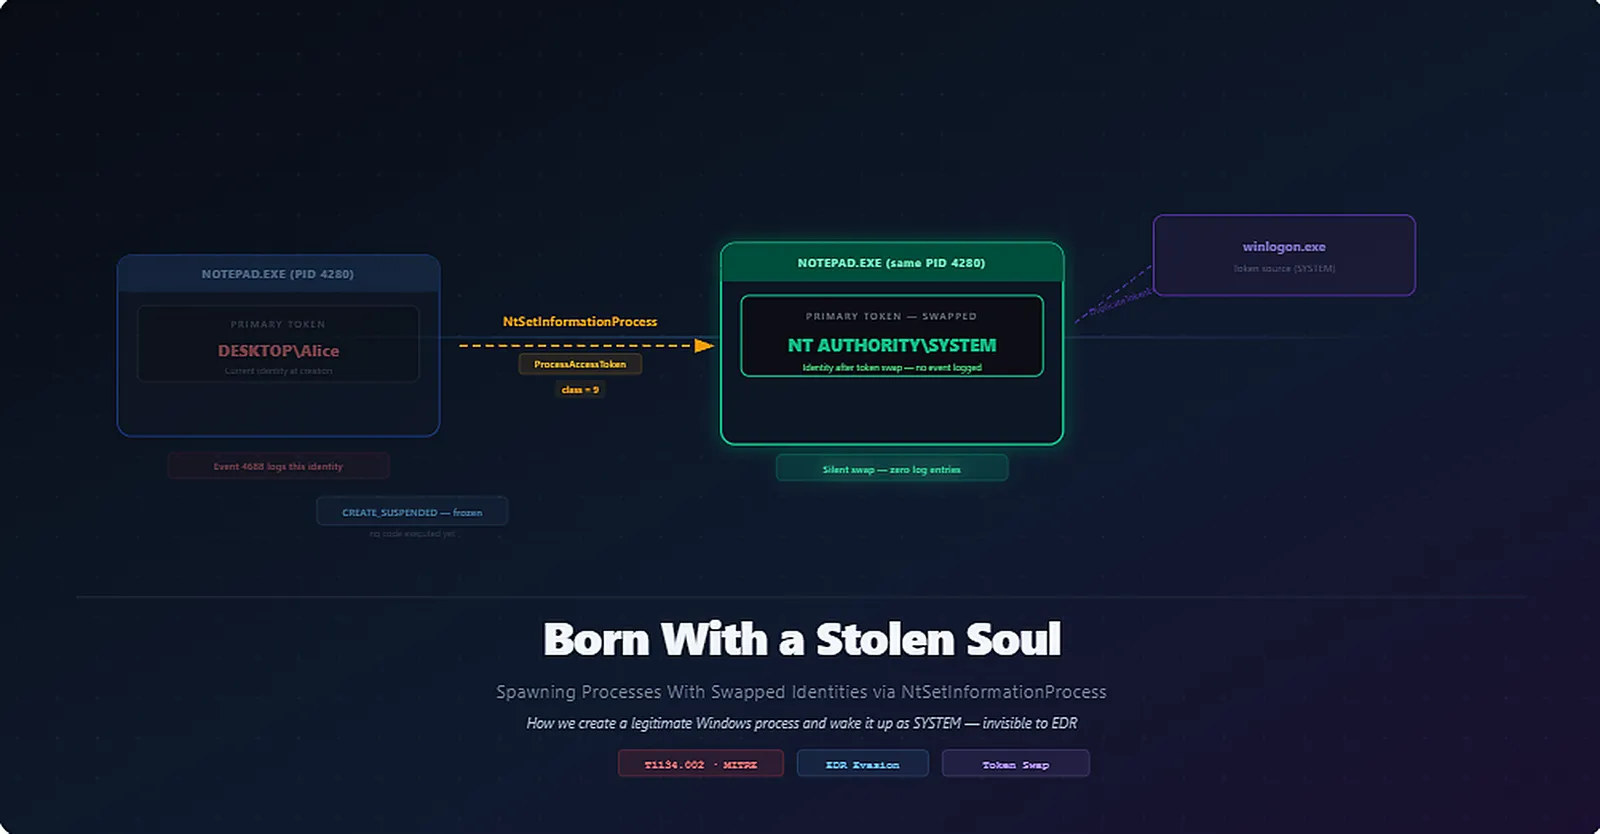
How we create a legitimate Windows process, replace its identity before it executes a single instruction, and wake it up as SYSTEM — invisible to most EDR…
Let's break down what adversary simulation actually is, how a simulation team moves through an organization stage by stage, and how each of those stages maps…